

Yes, you can ask a hotel to erase your personal data under GDPR Article 17, but the right is conditional, not automatic. Hotels often must keep some records for legal reporting or safety duties, so complete deletion is not guaranteed. A hotel must acknowledge your request and generally respond within one month, though the outcome may be partial erasure or anonymization rather than full removal.
TL;DR:
- Many hotel records are legally required to be retained long after a guest requests deletion, including identity documents and safety reports.
- A hotel must respond within one month to an erasure request, but full deletion may not be possible if legal obligations or safety concerns apply.
- Clear, specific requests citing the relevant GDPR ground and providing detailed stay identification speed up the response process.
- When deletion is granted, hotels should either fully delete or anonymize data and notify third parties when feasible; backups may retain data temporarily.
- Refusals often rely on legal retention duties, and guests can escalate by requesting detailed explanations or filing complaints with supervisory authorities.
Table of Contents
- What the right to erasure covers for hotel guests
- Hotel-specific exceptions and constraints on erasure
- How to make an effective erasure request to a hotel
- What hotels must do after receiving an erasure request
- If the hotel refuses your erasure request
- Practical tips and a checklist for guests
- Practical examples of data hotels hold that guests ask to erase
- How erasure requests can affect your stay and future bookings
- Balancing erasure rights with security and fraud prevention
- Why clean record-keeping protects both guests and hotels
- EuroCheckin: helping hotels manage compliance and guest requests
- FAQ
- Sources
What the right to erasure covers for hotel guests
Article 17 of the GDPR gives you the right to ask a hotel to delete personal data under specific conditions. We find it helps to know the exact grounds before writing a request, since citing the right one makes a hotel’s legal team respond faster and more clearly.
You can request erasure when:
- Your data are no longer necessary for the purpose the hotel originally collected them for.
- You withdraw consent and no other legal basis for processing exists.
- You object to processing and the hotel has no overriding legitimate grounds.
- The hotel processed your data unlawfully in the first place.
- A legal obligation under EU or national law requires erasure.
- The data were collected from a child without proper consent.
Erasure is different from the right to access or rectification: access lets you see what a hotel holds about you, and rectification lets you correct inaccurate details, while erasure asks for removal altogether. According to Article 17, the right is limited by specific exceptions, which is why a hotel’s answer to an erasure request is rarely a simple yes or no.
Hotel-specific exceptions and constraints on erasure
Hotels sit under extra legal duties that general businesses do not, and those duties often beat an individual’s erasure request. Guest registration rules require properties to record identity details and, in many cases, report them to police or tourism authorities. The AEPD’s guidance on the right to erasure confirms that retention required by law is a valid reason to refuse or delay deletion.
National hospitality rules, such as Real Decreto 933/2021, create mandatory guest-registration obligations that a hotel cannot sidestep just because a guest asks. These duties typically cover a defined retention window, after which the hotel should delete or anonymize the data on its own.
Data categories hotels commonly retain despite an erasure request include:
- Identity documents submitted at check-in for police or registry reporting.
- Records already transmitted to public safety authorities.
- Accounting and tax records tied to the stay, kept for statutory retention periods.
- Security logs connected to an active investigation or legal claim.
How to make an effective erasure request to a hotel
A well-written request moves faster through a hotel’s compliance process. We recommend following these steps in order.
- Find the hotel’s data protection contact, usually listed as a DPO email or on its privacy policy, and address the request there instead of a general booking inbox.
- State clearly that you are exercising your right to erasure under Article 17 of the GDPR and name the specific ground that applies to you.
- Include enough detail to identify the stay: full name, dates, booking reference, and the email or phone number used at booking.
- Avoid sending copies of your ID unless the hotel specifically asks, since the AEPD warns against requesting unnecessary identity documents for verification.
- Send the request by a method you can prove, such as tracked email or registered mail, and keep a copy.
- Note the date you sent it, since the hotel has one month to respond under Article 12(3) GDPR, extendable by two months for complex cases if it tells you within the first month.
Pro Tip: Ask the hotel to confirm, in writing, the specific legal basis for any data it keeps rather than accepting a vague refusal.
What hotels must do after receiving an erasure request
Once a hotel accepts that erasure applies, it faces technical and procedural obligations beyond simply pressing delete. We think guests benefit from knowing what a proper response actually looks like.
- Where full deletion is not possible for legal reasons, the hotel should anonymize the data so it can no longer be tied to you personally.
- Under the reasonable-steps duty tied to Article 17, the hotel must notify any third parties it shared your data with, such as booking platforms or payment processors, when feasible.
- Backups and archives present a technical limit: copies may persist briefly until a scheduled backup cycle overwrites them, and the EDPB’s coordinated enforcement report found this is a recurring difficulty across controllers.
- The hotel should explain clearly what was deleted, what remains, and why, rather than issuing a blanket confirmation.
If the hotel refuses your erasure request
A refusal is not the end of the process. Ask the hotel for a written explanation citing the specific legal basis and how long it intends to retain the data. If the response is late or vague, you can point to the one-month deadline in Article 12(3) as grounds for escalation.
- File a complaint with your national supervisory authority, such as the AEPD in Spain, including your original request and the hotel’s reply.
- Keep every email, tracking receipt, and date in one file before you file, since enforcement bodies ask for a clear timeline.
- Expect outcomes ranging from an erasure order to corrective measures or, in persistent cases, fines, consistent with patterns the EDPB’s 2025 enforcement review describes across supervisory authorities.
Practical tips and a checklist for guests
A tight, specific request gets a faster and clearer answer than a general complaint.
- Keep the message short, cite Article 17 directly, and include your stay dates and booking reference.
- Save a copy of everything you send and every reply you receive.
- Ask for anonymization or restriction instead of full deletion when a hotel has a legitimate retention duty, and request that it notify any third parties involved.
Pro Tip: Send your request through a channel that gives you proof of delivery, and note each follow-up date so you can show a clear timeline if you later file a complaint.
Practical examples of data hotels hold that guests ask to erase
Guests most often ask hotels to delete four kinds of records. Booking history, including dates, room type, and payment method, sits in the property management system long after checkout and is a common first target for erasure requests. CCTV footage from lobbies, parking areas, or corridors is trickier: hotels often keep it for a fixed security retention window, and a request to delete footage tied to an active incident will likely be refused on legal-claim grounds.
Loyalty program data, such as points balances, stay history, and preferences, is usually easier to erase fully since it exists for marketing and service purposes rather than legal reporting. Contact details used for post-stay marketing emails fall into the same category: once you withdraw consent, a hotel generally has no remaining basis to keep sending them.
Identity documents collected at check-in sit at the other end of the spectrum. Where national guest-registration rules apply, hotels frequently cannot erase this category until a statutory retention period ends, regardless of your request. Knowing which bucket your data falls into before you write helps you ask for the right remedy, whether that is deletion, anonymization, or simply stopping a specific use like marketing.

How erasure requests can affect your stay and future bookings
Granting an erasure request rarely disrupts a stay already completed, but it can change what a hotel can offer you later. Once loyalty data is deleted, points balances and stay history disappear with it, so a returning guest may lose status or rewards tied to that account.
Removing contact preferences can mean losing early access to offers or room upgrades a hotel previously sent based on past stays. If you ask a hotel to delete contact details entirely, it may no longer be able to reach you about booking confirmations for a future stay made under the same profile, so it helps to specify that you want historical data erased while keeping an active, separate booking untouched.
For the hotel, a surge of erasure requests without a clear internal process can slow down guest service generally, since staff have to manually trace records across property management, loyalty, and marketing systems. Hotels running on fragmented, partly manual record-keeping take longer to confirm what they hold, which delays both the guest’s answer and routine service tasks elsewhere.
Balancing erasure rights with security and fraud prevention
Hotels are not just data holders. They are also targets for fraud, chargebacks, and occasionally safety incidents, which is why some retention is a legitimate counterweight to erasure requests rather than a convenient excuse. Reporting obligations tied to guest registration exist precisely so authorities can act quickly if a crime or safety issue arises during a stay.
A hotel asked to erase payment or identity data tied to an open fraud investigation can lawfully refuse under the legal-claims exception in Article 17. The same logic applies to CCTV footage connected to an active incident report. Where no such conflict exists, though, there is no good reason to hold onto data beyond its original purpose, and a hotel that does so anyway is exposed to exactly the kind of enforcement issue the EDPB’s 2025 report flags as a recurring problem.
The practical balance is specificity: a hotel should be able to name the exact legal basis for every category of data it keeps past a guest’s request, rather than defaulting to a blanket retention policy that covers everything indiscriminately.

Why clean record-keeping protects both guests and hotels
Hotels that handle guest registration manually make more errors, both in what they report to authorities and in what they can tell a guest about their own data. We believe the fastest, most lawful erasure responses come from properties that can trace exactly which record exists, why, and under which legal basis, rather than searching across spreadsheets and paper logs. A digital guest register that documents retention reasons at the point of check-in turns a stressful request into a quick, defensible answer for everyone involved.
— Sofía Herrera
EuroCheckin: helping hotels manage compliance and guest requests
For hotels and property managers reading this from the other side of a request, we built EuroCheckin to turn guest registration from a manual burden into an automatic, documented process. Our platform reports guest data straight to SES Hospedajes in line with Real Decreto 933/2021, with every record hosted securely within the European Union.
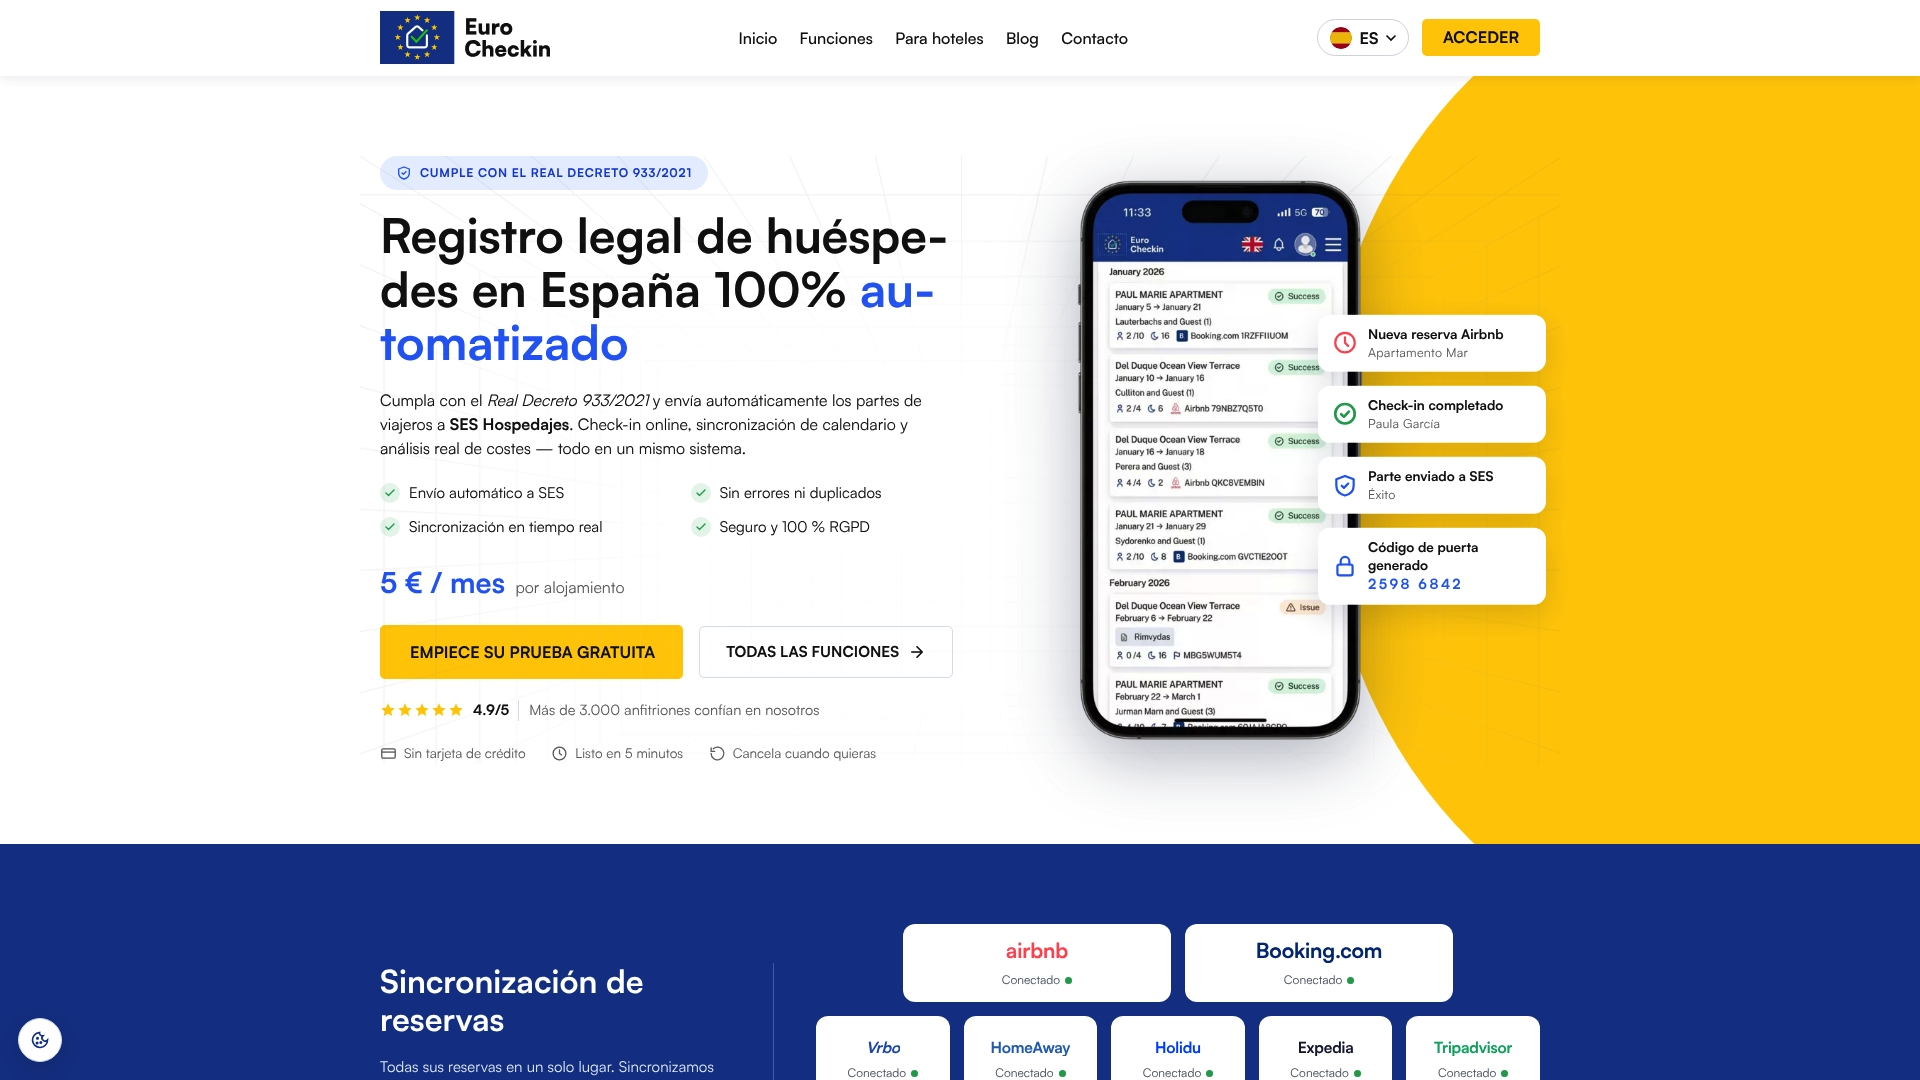
Because each entry carries a clear retention reason from the moment a guest checks in, responding to an erasure request becomes a matter of looking up the record instead of chasing down scattered files. Our plan for hotels starts from 3 EUR per month per room, with a free trial available. If you manage a property and want fewer manual errors alongside faster, better-documented responses, visit our hotel compliance page to see how it works for your property.
This article is general information, not a substitute for advice from a qualified lawyer. Consult a qualified legal professional about your own circumstances before acting on anything here.
FAQ
What are the exemptions to the right to be forgotten?
The GDPR exempts erasure when processing is necessary for legal obligations, public interest, archiving or research, exercising legal claims, or freedom of expression, as set out in Article 17(3). For hotels, the most common exemption is a statutory guest-registration or reporting duty that requires keeping certain records for a defined period.
What is the 15/5 rule in hotels?
This is not a recognized GDPR or hospitality data protection rule, and no primary source in this article defines it. If you encountered the term elsewhere, it likely refers to an unrelated hotel operations practice rather than a legal retention standard.
Does Europe have the right to be forgotten?
Yes, the right to erasure is enshrined in Article 17 of the GDPR, which applies across the European Union, including to hotels processing guest data. It is a conditional right, limited by exceptions such as legal obligations and public interest, rather than an absolute guarantee of deletion.
Can I claim the right to be forgotten on Google in the UK?
This article covers GDPR erasure requests to hotels under EU law, and UK search-engine delisting follows separate post-Brexit data protection rules outside that scope. For a hotel stay within the EU, your erasure rights run through Article 17 of the GDPR and the hotel itself, not through a search engine.
Sources
- Regulation (EU) 2016/679 — Article 17 (Right to erasure)
- EDPB — Coordinated enforcement report: Implementation of the right to erasure (2025)
- AEPD — Derecho de supresión (‘al olvido’)